53+
Trusted By Leading Enterprises Worldwide
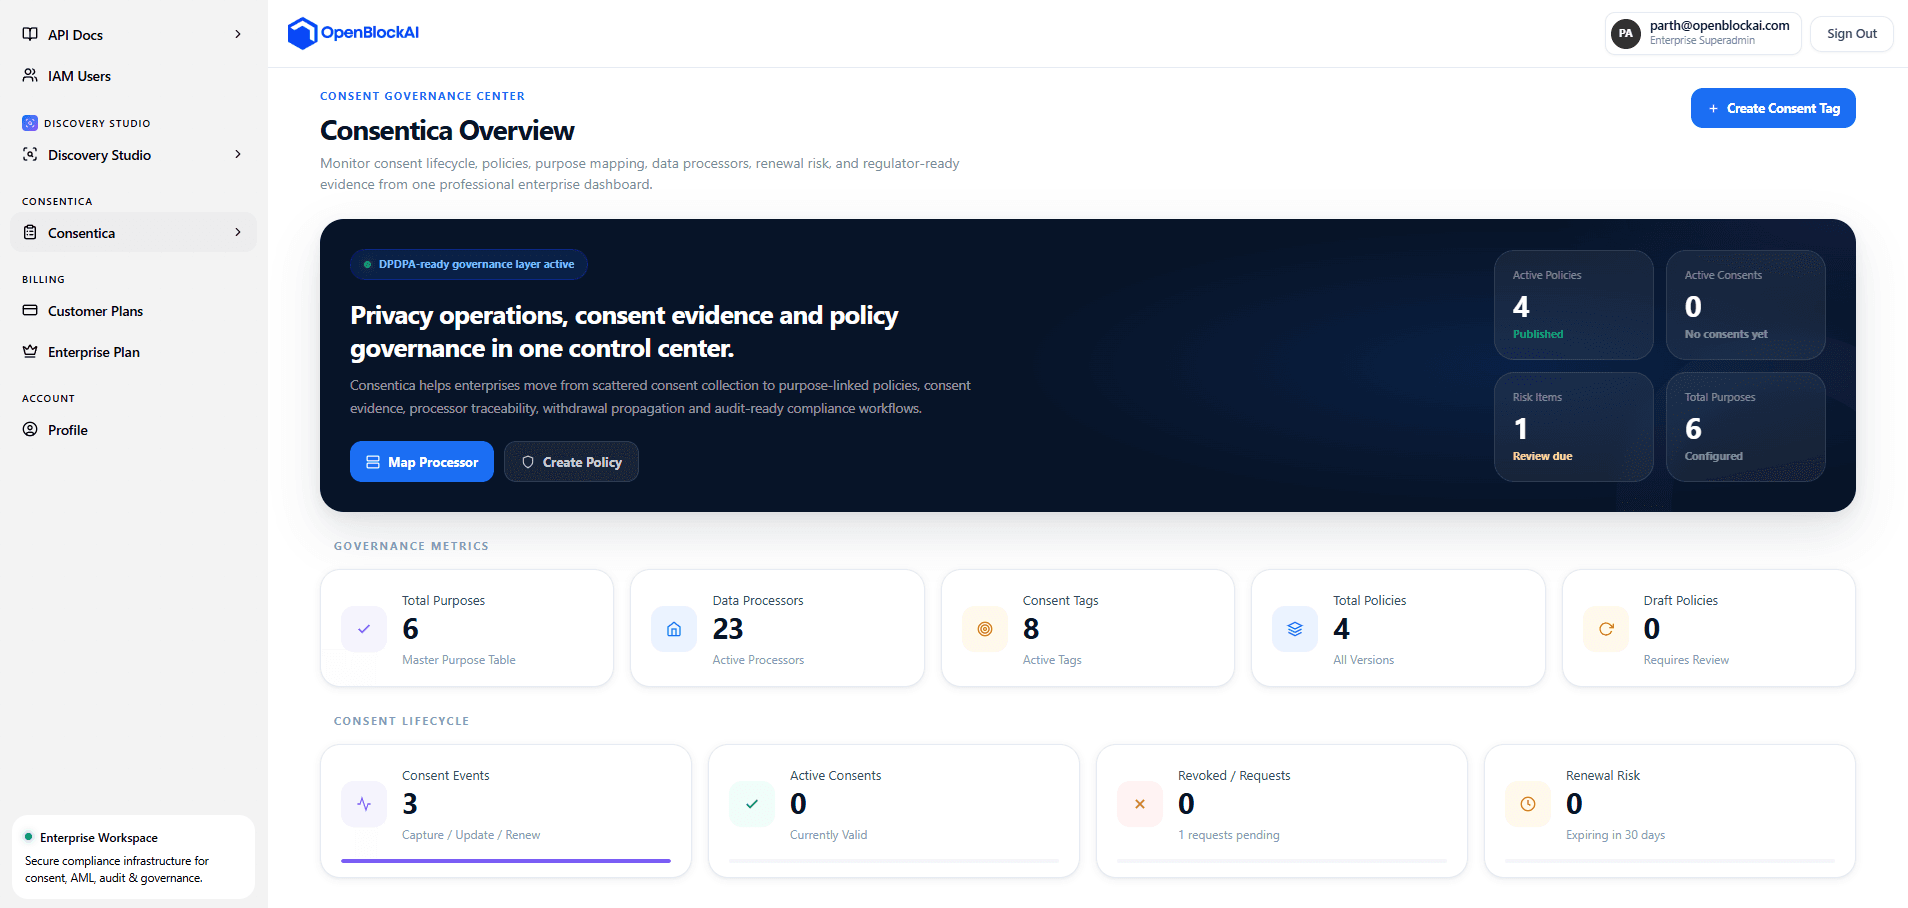
Consentica — Consent Management Platform
Create purpose-specific notices, capture consent across digital and assisted journeys, keep the latest consent status synchronised across internal systems and processors, and maintain verifiable evidence from consent to withdrawal.
Trusted By Leading Enterprises Worldwide
Trusted Partners
Compliance regions covered
Consumers supported
Define processing purposes, personal data categories, notice content, mandatory and optional choices, validity periods and policy versions before consent is presented.
Maintain one current permission state for every customer and purpose, enabling applications, business systems and processors to act on the latest consent decision.
Preserve verifiable evidence of the notice shown, purpose requested, language, channel, customer choice, timestamp, policy version and every subsequent change.
Create versioned notices linked to purposes, personal data fields, processors and consent validity.
Launch consent across web, mobile app, QR, branch, call centre, IVR and assisted journeys.
Present clear choices in English and 22 Scheduled Indian languages.
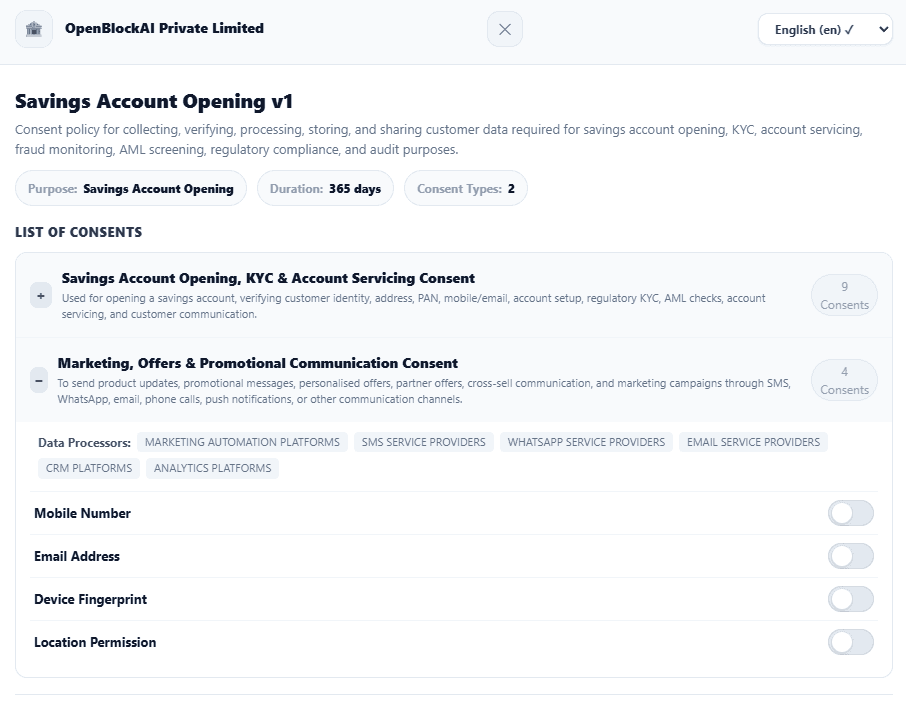
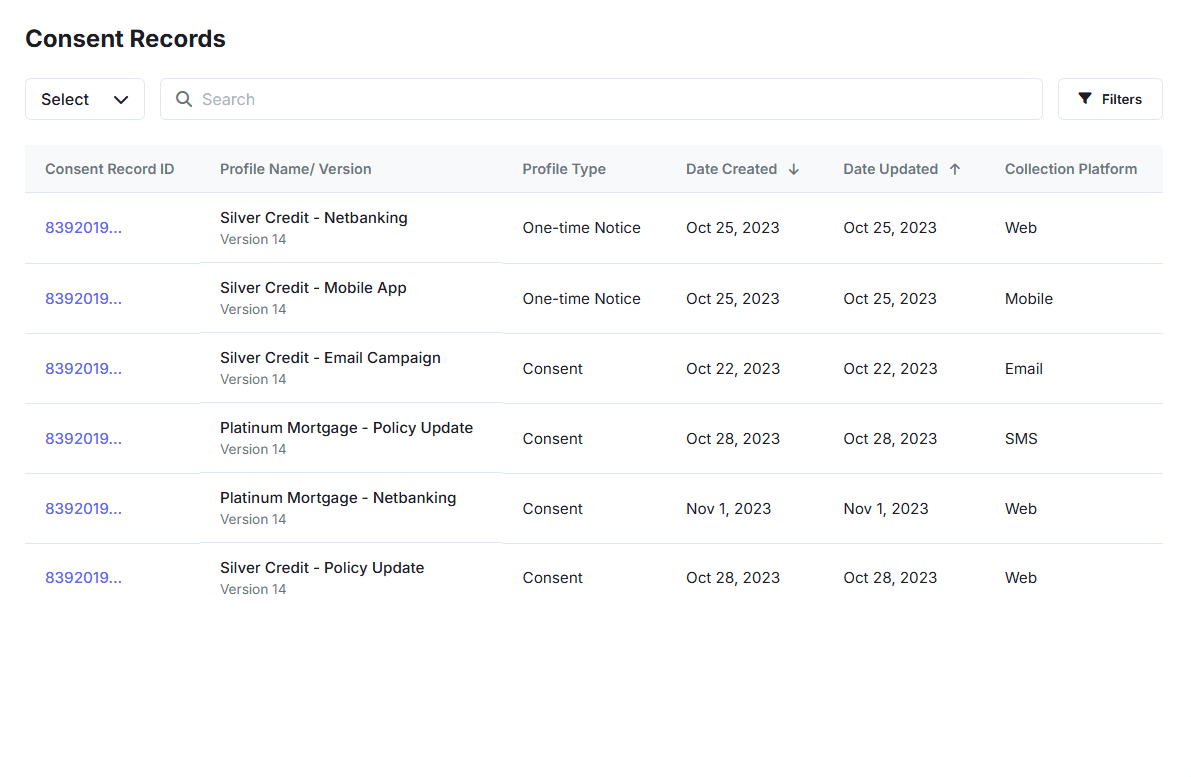
Let customers view, manage and withdraw purpose-level permissions through the Privacy Centre.
Propagate the latest consent state through APIs, webhooks and connected systems.
Trigger cessation, suppression, deletion or review workflows according to applicable purpose and retention rules.
Apply age checks before beginning the intended processing journey.
Verify that the parent or guardian is an identifiable adult through reliable identity, age or DigiLocker-supported flows.
Link the approval to the child, purpose, notice version, verification method and timestamp.
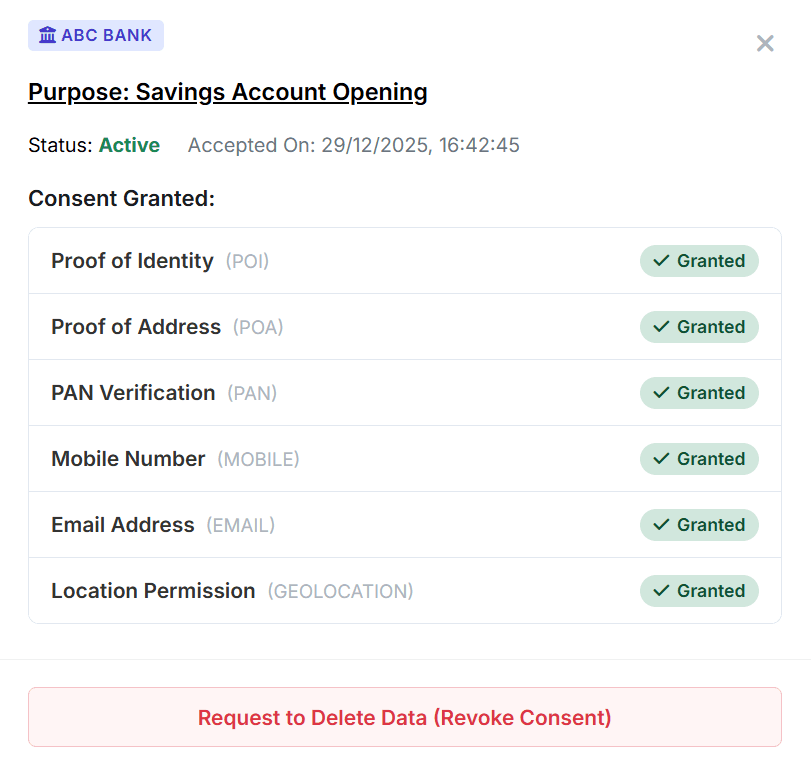
Real-time Consent Check and Record APIs, webhooks and system integrations.
SaaS, VPC or on-premises deployment options.
Role-based access, tenant segregation, monitoring and audit logs.
High availability and configurable enterprise SLAs.
See how organisations use OpenBlockAI to improve data visibility, strengthen governance and reduce the manual work behind compliance.
Consentica made a complex privacy implementation feel manageable. Their business and support teams worked closely with us throughout the rollout, and we always had clarity on what needed to happen next.
Earlier, consent information was scattered across different journeys and systems. Consentica gave us one place to see what a customer agreed to, which policy version applied, and what changed when consent was withdrawn.
The important part for us was not simply capturing consent. Consentica helped us make the latest consent status available to our applications and downstream systems without building separate workflows for every channel.
We no longer have to piece together screenshots and logs when consent evidence is requested. The notice, purpose, language, policy version, timestamp and complete status history are available together.
We believed we already knew where our personal data was stored. Discovery Studio uncovered information across spreadsheets, shared drives, internal applications and vendor processes that had never appeared in our existing inventory.
As a multi-tenant SaaS platform, every customer wanted their own consent language and notice rules. Consentica let us configure that per tenant without forking our codebase for each one.
Discovery Studio did not feel like another compliance questionnaire. It helped our business, technology and privacy teams connect data categories, purposes, systems, owners and vendors in one structured workspace.
The endpoint and repository scans gave us a clearer view of personal data outside our core systems. That evidence made our data mapping far more accurate and helped us prioritise the gaps that required immediate attention.
The real value came after discovery. We could turn the findings into practical RoPA inputs, DPIA triggers, vendor actions and an implementation roadmap instead of being left with another static assessment report.
We expected months of integration work before going live. Consentica needed zero integration to launch, and our care teams now process patient consent withdrawal requests in minutes instead of routing them through IT.
Our vendor footprint across plants and suppliers made governance messy. Consentica gave us one view of which vendors hold what data under which consent, so vendor governance stopped being a spreadsheet exercise.
Most of our personal data was buried in support tickets, chat logs and unstructured files no one had mapped. Discovery Studio surfaced it and gave us a defensible starting point for our data inventory.
From notice design to withdrawal handling to audit evidence, Consentica stayed with us end-to-end — support was there whenever a compliance deadline got tight across our booking and loyalty platforms.
Start without integration. Manage unlimited consent events. Get your early-access workspace configured within 48 hours. Experience one complete consent journey—from purpose and notice configuration to capture, withdrawal, downstream status and audit evidence.
A privacy specialist reviews your use case.
We map one customer journey, including purposes, channels and consent requirements.
We configure the notice, consent choices, language and workflow.
Your early-access workspace is ready within 48 hours—no integration required to begin.
Still have questions? Book a demo — we’ll map your consent flow in 15 minutes.
Under India’s DPDP framework, a Consent Manager is an entity registered with the Data Protection Board of India (DPB) that provides an accessible, transparent, and interoperable platform to help users give, manage, review, and withdraw consent.
In simple terms: it acts as a trusted consent layer that helps users control how their personal data is used—while giving organizations a cleaner, auditable way to operationalize consent management.
You generally need valid consent when you are processing personal data and your use case does not fall under a permitted ground or other legally allowed basis under the DPDP framework.
Best practice: always show a clear notice covering what data is being collected, why it is needed, and how long it will be used for—then collect granular consent and make withdrawal as easy as opt-in.
The Digital Personal Data Protection Rules, 2025 were notified in November 2025, but they do not all start at once.
The rollout follows a staggered commencement. Some provisions came into force immediately on publication, while others take effect later—such as certain obligations beginning one year or eighteen months after notification.
For organizations, the practical takeaway is simple: become production-ready now by mapping data flows, standardizing notices and consent records, setting up DSR workflows, and making audit logging a default part of operations.
The DPDP framework uses a penalty schedule where the Data Protection Board of India determines penalties based on the nature, severity, and impact of the contravention.
The practical takeaway: build strong security, clean consent governance, and audit-ready proof from day one.
The DPDP framework does not explicitly use the word “cookies”, but if cookies, trackers, or similar technologies can identify a person or enable profiling, they may amount to personal data processing in practice.
A safer approach—especially if you use analytics, advertising, or third-party scripts—is to:
If you only use strictly necessary cookies, such as session or authentication cookies, you can still disclose them transparently even if the journey is not gated behind an opt-in step.
OpenBlockAI helps organizations operationalize DPDP-ready consent management across digital and assisted journeys:
OpenBlockAI brings unified AI-driven compliance to your entire financial ecosystem - powered by real-time detection, global pattern intelligence, and privacy-preserving collaboration across networks.
Discover, classify and map personal data across every system — then turn it into audit-ready RoPA, DPIA, vendor governance and evidence records. Built for GDPR, DPDPA, HIPAA and beyond.
Capture, govern and prove customer consent across every channel — fully auditable across every connected system. Built for GDPR, HIPAA, DPDPA and beyond.
Vault, tokenise, and govern PII with enterprise-grade encryption and access control - purpose-built for privacy-first data infrastructure across networks.